Every campaign, reminder or code a company sends by SMS starts with a piece of personal data: the customer’s mobile number. Since March 2025, Mexico has a new Federal Law on the Protection of Personal Data Held by Private Parties (LFPDPPP), and although its regulations have not yet been published, the law is already binding. Here is what changed and what to review in your contact lists.
What changed with the new law
- It was published in the Official Gazette on March 20, 2025 and took effect the next day, replacing the 2010 law.
- INAI was dissolved: supervision and sanctions on personal data moved to the Ministry of Anti-Corruption and Good Governance (Secretaría Anticorrupción y Buen Gobierno). Privacy notices that still mention INAI are out of date.
- The law formalizes retention periods: data must be blocked and then deleted once it is no longer needed for the purpose that justified collecting it.
- Fines range from 100 to 160,000 UMA for minor violations and from 200 to 320,000 UMA for serious ones, and can double when sensitive data is involved.
- The new regulations were due within 90 days, but by mid-2026 they were still pending, so companies must comply based on the law itself.
What to review in your SMS lists
- Privacy notice. It should state that the number will be used to send messages, for which purposes (operational, service or promotional) and how to exercise ARCO rights. Update the reference to the authority.
- Separate purposes. A payment notice or an OTP code is not the same as a promotion. For marketing messages, consent rules and opt-out registries also apply, as explained in SMS marketing regulations in Mexico.
- Effective opt-outs. If someone replies “STOP” or asks not to receive more messages, they must leave the list immediately and not come back with the next upload. Blacklists on the sending platform make this automatic.
- Retention periods. Define how long you keep numbers from former customers or finished campaigns, and clean them up.
- Providers as processors. Your SMS platform processes data on your company’s behalf: the contract should set out confidentiality, security measures and what happens to the data when the relationship ends.
- Security. Prefer encrypted connections, per-user access and activity logs. Avoid passing lists around in spreadsheets by email.
An opportunity, not just an obligation
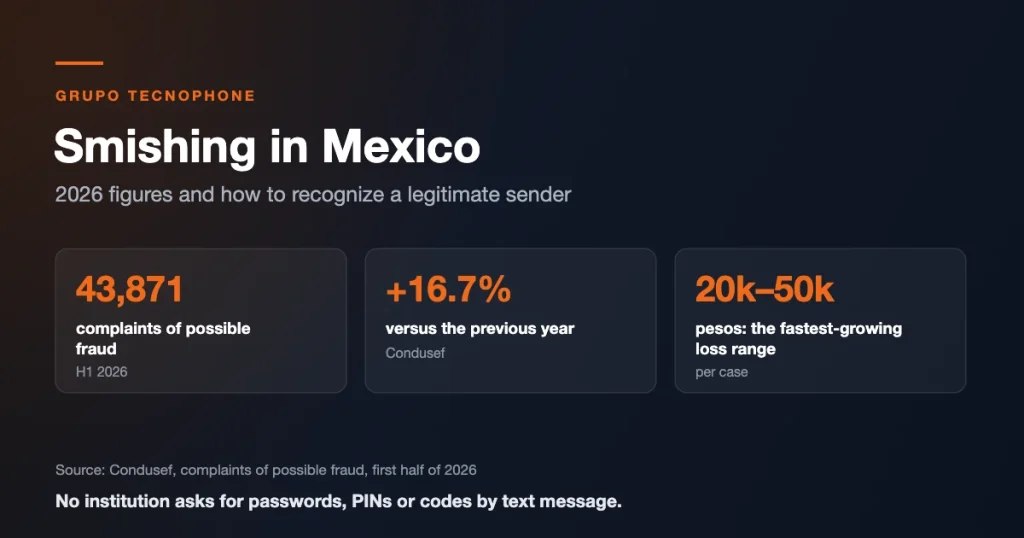
Companies that take care of their contact lists get more than compliance: cleaner lists, better delivery rates and customers who trust their messages. With more SMS fraud around, that trust is an asset. And with the CRT’s new anti-spam rules in the works, getting your data in order today saves adjustments tomorrow.
This article is for information only and does not constitute legal advice. For specific cases, consult a data protection specialist.
At Grupo Tecnophone we provide blacklists, opt-out handling, encryption and real-time reports so your SMS sending is orderly and traceable. If you want to review it with your own operation, request a demo.
Sources
- “Ley Federal de Protección de Datos Personales en Posesión de los Particulares (current text)”, Chamber of Deputies of Mexico. Read article
- “LFPDPPP: guía de la nueva ley de protección de datos de México”, Adopt. Read article
- “Nueva LFPDPPP: reglamento pendiente en 2026”, SharkIT. Read article